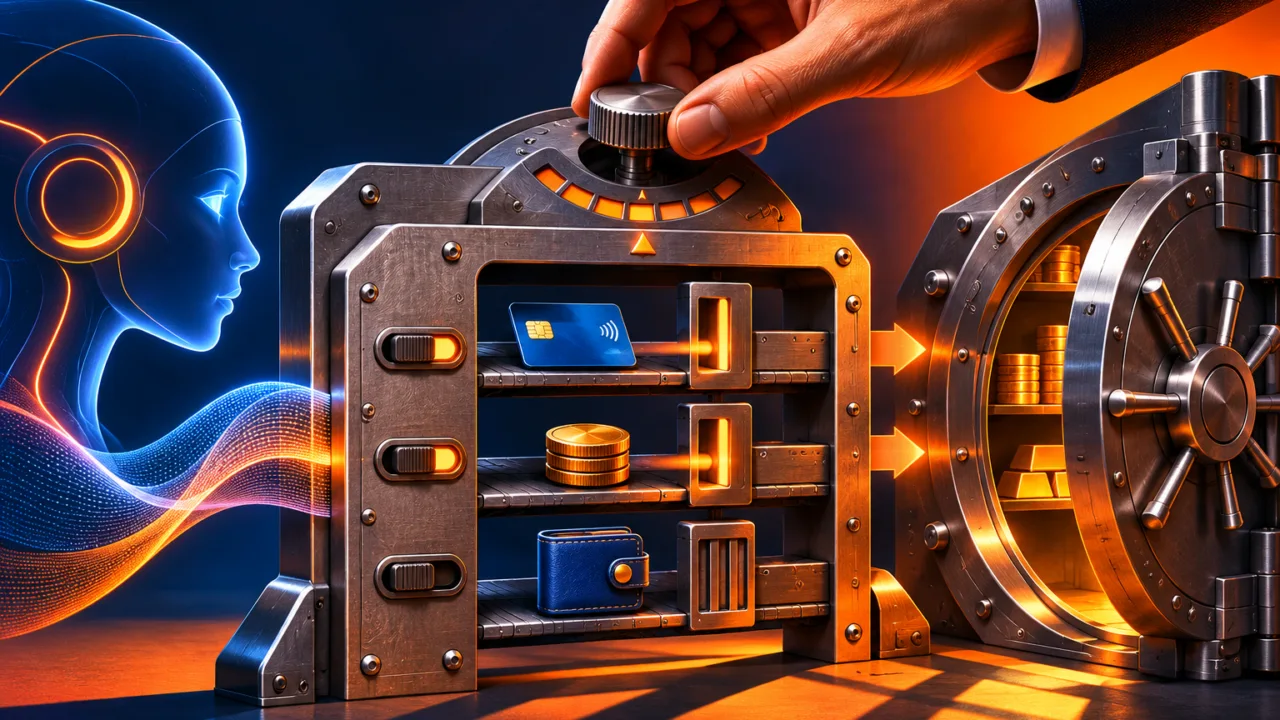
AI agents can already interact with crypto wallets, prepare transactions and, depending on how they are configured, trigger payments. By 2027, the key question will not simply be whether this is technically possible. It will be who controls the authorization chain: who holds the keys, who sets the limits and who can stop the system when an instruction leads to an unwanted expense.
A conversational application does not become safe simply because it accurately describes your intent. Between the request and the payment sit a model, tools, a signer and a network. This guide examines their respective roles based on documents reviewed on November 13, 2026. It does not guarantee any provider’s future availability or recommend delegating savings to an autonomous agent.
In brief
- An agent can use a payment tool without its private key appearing in the conversation or the model’s context.
- Effective limits must be enforced at the execution layer, rather than relying solely on written instructions given to the assistant.
- Per-transaction caps, cumulative budgets, approved destinations and revocation address different risks; no single control is sufficient on its own.
AI agents and crypto wallets: distinguishing the four roles
Our crypto ecosystem glossary distinguishes a wallet from the asset it allows someone to control. In an agentic application, four additional functions must be considered: interpreting the request, proposing an operation, checking its authorization and signing it. A single interface can conceal these functions without making them equivalent. Separating them helps identify where an error could still be stopped.
The model produces a proposal based on the information it receives. A tool may then convert that proposal into technical parameters: network, recipient, asset, amount and call data. The authorization component checks what remains permitted. Finally, the signer commits the rights associated with the account, depending on the architecture. Identifying these stages prevents an intent expressed in text from being treated as a transaction that has already been controlled.
The question “Does the AI own the wallet?” is therefore too imprecise. An agent may know a public address without being able to sign. It may also have limited access to a service that signs under specific conditions. Conversely, a poor configuration can give it far broader powers than the conversation suggests.
Before trying a product, ask for a diagram showing these roles and an example of a rejected transaction. Who rejects an excessive amount? Which component blocks an unapproved destination? An answer focused solely on the model’s quality leaves authorization unresolved. The documentation should demonstrate effective control, not merely claim that the assistant understands your limits.
What the available tools actually demonstrate
The official Coinbase AgentKit project provides tools for connecting agents to wallets and blockchain actions. It also includes examples of human controls. This documentation establishes that integration is technically possible; it does not show that every application using the project automatically has a policy suited to your situation.
Coinbase’s Agentic Wallets page describes per-transaction and per-session limits, as well as isolating keys from the model’s context. These are features announced by the provider. In a real deployment, their configuration, scope and behavior in the event of an error still need to be checked in the selected version.
Another class of architecture relies on programmable accounts. The ERC-4337 specification notably allows an account to define its own validation logic. It does not create a universal security policy for every wallet. The rights actually granted still depend on the code, modules and parameters used in the implementation.
These examples are enough to establish technical feasibility without promising risk-free autonomy. Nor do they justify looking for a token bearing an assistant’s name. Using a service, buying a token and holding a claim against a provider are different activities. A commercial name does not prove any particular economic right.
Setting a budget that can withstand repeated payments
A per-transaction cap prevents an individual payment from becoming too large, but it does not necessarily limit total spending. In a hypothetical example, twenty payments of four euros amount to eighty euros. Each payment would nevertheless remain below a five-euro cap. The example shows why total spending over a defined period must also be controlled.
The cumulative budget must specify which expenses it includes. Does it cover network fees and conversions? Is it shared across several agents? What happens when two operations arrive at the same time? An interface displaying a balance does not automatically answer these questions. Testing should cover scenarios close to the limit, not just a normal payment.
The time period matters just as much as the amount. A per-session limit requires a definition of the session, its expiration and its renewal. If a program can open new sessions without approval, a local cap does not guarantee a global budget. Do not assume how a provider handles this: consult its documentation and test the relevant conditions.
A separate reserve reduces exposure without replacing the other controls. A test wallet should not also serve as a savings vault. The limitations of hardware wallets show that strong key protection does not validate the meaning of a transaction. Signer security and spending control remain two separate issues.
Finally, set an operational stop threshold. A succession of failures, unusual consumption or repeated requests should trigger a review. This threshold can be measured by number of operations, cost and time. The goal is not to let a loop continue until the balance is exhausted and then treat that loss as the only possible limit.
An approved address does not make every interaction acceptable
A recipient allowlist can reduce the risk of sending funds directly to an unknown address. It does not show that every function of an approved contract is appropriate for your needs. A simple transfer, a spending approval and a lending operation do not grant the same rights. Controls must cover the action, not just the address.
The parameters therefore deserve review before signing. Check the network, asset, amount and beneficiary, along with any permissions granted when the context requires it. An operation presented as a connection may have a different scope. Do not let the description generated by the same agent serve as the only evidence of what will actually be executed.
OWASP recommends independent validation of sensitive actions for agents. Its approach distinguishes tool permissions, untrusted inputs and high-impact actions. These general recommendations do not constitute an audit of your wallet, but they provide a useful basis for reviewing the architecture and abuse scenarios.
An external source may contain a malicious instruction. OWASP describes the risk of prompt injection and recommends keeping authorization outside the model’s sole control. A page consulted to obtain a price must not become a new authority capable of changing the agent’s financial mandate.
The differences between self-custody and delegated custody also clarify each participant’s responsibility. Ask who holds the secrets and which operations the provider can perform. An answer about the technology used does not replace contractual terms or recovery and claims procedures.
Test revocation before funding the service
A visible stop button does not prove that every authorization has been stopped. It may interrupt one interface while leaving other components active. Testing must therefore establish what changes in practice: whether a session is closed, access is removed, a permission expires or obtaining a new signature becomes impossible. The documentation should specify the mechanism’s limits.
Start in a test environment whenever the service allows it. Have the system accept an authorized operation, then reject an amount above the limit and an unapproved destination. Also check its behavior after expiration or revocation. The aim is to observe the expected refusals without committing significant value to a system you do not understand.
Revocation may not cancel a transaction that has already been broadcast or an obligation that has already been created. This distinction should appear in the report. Ask what the system can still prevent when the alert arrives. Presenting a stop mechanism as a time machine would create a false sense of protection.
Logs should make it possible to understand the request, the authorization decision and the operation executed without recording secrets. Precautions concerning personal data and identity checks also remain relevant when the tool collects information about the account holder. A usable history does not justify excessive sharing of sensitive data.
Also prepare a manual fallback. If the model or provider becomes unavailable, who controls pending operations? Which document shows the payments already made? Useful automation must leave the human operator with a comprehensible situation. Without that continuity, the initial time saving can turn into a lengthy reconstruction after an incident.
What level of autonomy should be used in 2027?
The choice should start with the narrowest need. Checking a balance requires no transfer rights. A payment can be prepared before human approval. Delegating small, repeated expenses requires suitable caps, a clearly defined scope and supervision. There is no reason to move directly to the highest level of autonomy simply because a product makes it possible.
Create a mandate sheet covering permitted actions, exclusions, amounts, periods, recipients and the stop mechanism. Link each rule to test evidence and a person responsible for it. Unconfirmed limits should remain visible. A commercial promise must not fill a missing technical validation step.
Reassess this sheet after any change to the model, connector, contract or provider. A new capability can alter exposure without changing the wallet’s appearance. Ongoing control must therefore track the components that actually act, not just the application name installed on your screen.
Agents may use crypto wallets in 2027, but their powers must remain explicit and verifiable. The decisive question is not whether they appear intelligent. It is what they can sign, what remains forbidden to them and how you retake control when their proposal no longer matches your mandate.