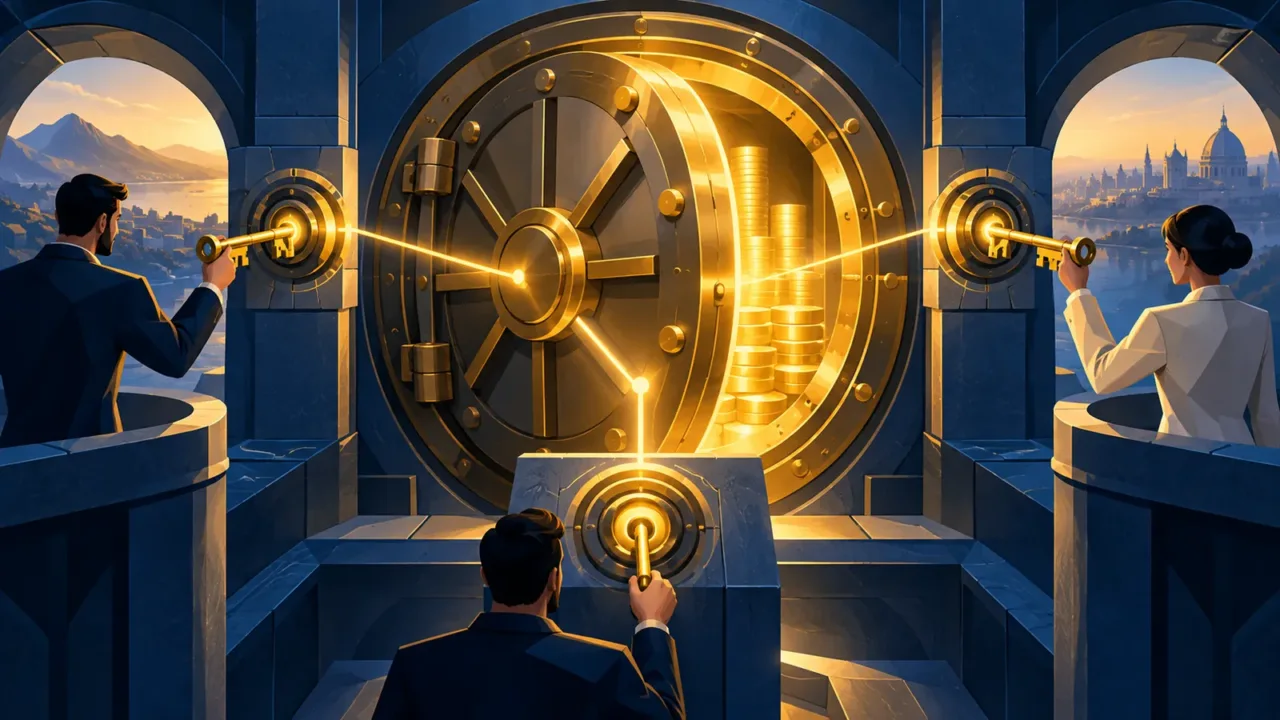
How a multisig threshold works
The BrefCrypto guide to wallets explains how key custody works. In a multisig setup, several owners or devices control the same policy. The threshold specifies the minimum number of signatures required.
With a 2-of-3 scheme, losing one key does not immediately lock the funds. However, two compromised keys are enough to authorize a spend. A 3-of-5 setup provides more redundancy, but also increases complexity, costs and the number of backups that must be managed.
On Bitcoin, the condition is defined in a script, and each signer produces a separate signature. On Ethereum, a smart account can apply comparable logic. Safe’s documentation on multisignature smart accounts describes a list of owners and a required threshold before execution.
Multisig is not two-factor authentication
Two-factor authentication on an exchange protects access to an account managed by a company. Multisig enforces an on-chain rule: the network rejects the transaction if the threshold has not been met. The two mechanisms therefore involve different forms of control and different remedies.
Two applications installed on the same phone do not provide genuine separation. Malware, theft or a hardware failure could affect both. Each key should be kept on an independent device or medium, ideally in a separate location.
Likewise, three copies of a single seed phrase do not create a 2-of-3 wallet. They simply reproduce the same key. A multisig setup uses different keys under a shared policy.
Choosing the right configuration
For an individual, 2-of-3 often offers a good balance: one active key, one personal backup and one key held by a third party or kept in another location. For a company, 3-of-5 can distribute control among management, finance, security and backup holders.
The threshold must withstand two opposing risks: theft and lockout. A threshold that is too low makes compromise easier. One that is too high makes the loss of a single key dangerous. Map out possible incidents before choosing: fire, death, internal conflict, travel, hardware failure or a signer’s unavailability.
Avoid storing all the keys in the same safe. Geographic separation matters as much as technical separation. For a company, also document who can replace a signer and what approval is required.
Backing up the keys and configuration
Every seed phrase requires an offline backup. The guide to the limitations of hardware wallets points out that the device does not replace this backup. Use durable storage media and avoid photos, emails or unencrypted cloud storage.
Multisig adds another element: the information needed to reconstruct the wallet. Depending on the software, this may include extended public keys, the descriptor, script, network, threshold and derivation path. Without this configuration, the seed phrases may not be enough to easily recover the funds.
Create several copies of the descriptor, since it generally cannot be used to spend funds on its own. Still, consider the privacy implications: it reveals the associated addresses. Keep it in controlled locations and document the restoration procedure.
Test before depositing a significant amount
Set up the wallet with a small amount. Send a transaction, collect the signatures on the designated devices, then broadcast it. Next, simulate the loss of one key and restore the wallet using the minimum number of remaining keys.
This test can reveal incompatibilities involving formats, firmware or the network. It also confirms that each signer understands their role. A procedure that has never been tested can fail at the worst possible time.
Repeat the test after a major software update or when replacing a device. Keep a small reserve for fees. On Ethereum, a smart account needs ETH on the correct chain to execute a transaction.
Managing transactions day to day
Define who prepares the transaction, who verifies the address and who broadcasts it. Each signer should independently check the amount, network, fees and destination on their own device. One person should not simply send the others a screenshot to approve without independent verification.
For a company, add a justification, invoice or internal identifier. A signature log makes audits easier. Set limits as well: small expenses can follow a faster process, while a large transfer should require additional checks or a delay.
The operating policy is what gives multisig its real value. Without one, several people can jointly approve the same well-presented fraud.
Technical and human risks
A multisig contract may contain a vulnerability or an upgrade function. Review the code, audits and enabled modules. A malicious plugin may sometimes bypass the normal workflow. On Bitcoin, compatibility between software and the storage of the descriptor require particular attention.
The risk of collusion remains: two signers in a 2-of-3 setup can act together. Coercion is also a risk. Distributing keys among people who are connected to one another does not guarantee genuine independence.
Crypto security for the years ahead must combine devices, procedures, confidentiality and incident response. No threshold can fix an organization that is poorly documented.
Planning for succession and disputes
Multisig facilitates a gradual transfer of control. An heir, notary or executor can hold one key without being able to move the funds alone. The other keys and instructions remain separate until death or incapacity.
This arrangement must comply with local law. A technical setup does not replace a will or settle legal ownership. The crypto and Bitcoin succession plan outlines the necessary documents, inventories and tests.
Also plan for disagreements between business partners. Who replaces a key? What vote authorizes the change? How are the funds protected during the dispute? These questions should be answered before a crisis.
Key takeaways
- Multisig distributes spending authority across several keys according to a threshold.
- Seed phrases are not always enough: the descriptor and configuration also need to be backed up.
- Restoration tests and an independent signing procedure matter just as much as the hardware.
More keys require better organization
Multisig eliminates a single point of failure, but adds responsibilities. A simple configuration, separate locations, a backed-up descriptor and regular drills create a robust system. Without documentation, protection can turn into lockout. The right threshold therefore depends on concrete risks and on people who can follow the procedure.